Your network contains an Active Directory domain named contoso.com that is federated to an Azure Active Directory (Azure AD) tenant. The on-premises domain contains a VPN server named Server1 that runs Windows Server 2016.
You have a single on-premises location that uses an address space of 172.16.0.0/16.
You need to implement two-factor authentication for users who establish VPN connections to Server1.
What should you include in the implementation?
Correct Answer:
B
You need to download, install and configure the MFA Server.
References:
https://docs.microsoft.com/en-us/azure/active-directory/authentication/howto-mfaserver-deploy
HOTSPOT -
You configure the Diagnostics settings for an Azure SQL database as shown in the following exhibit.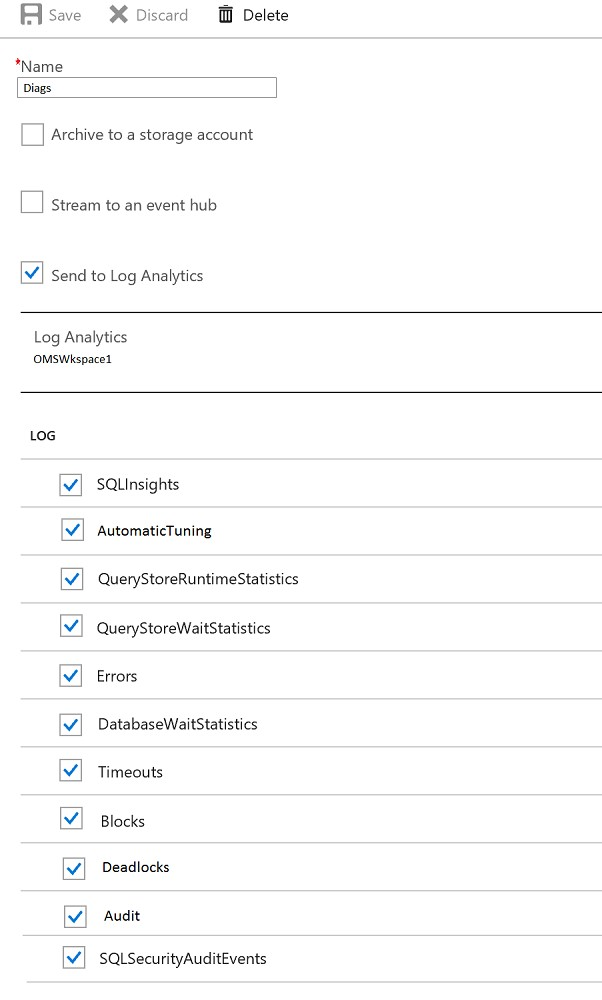
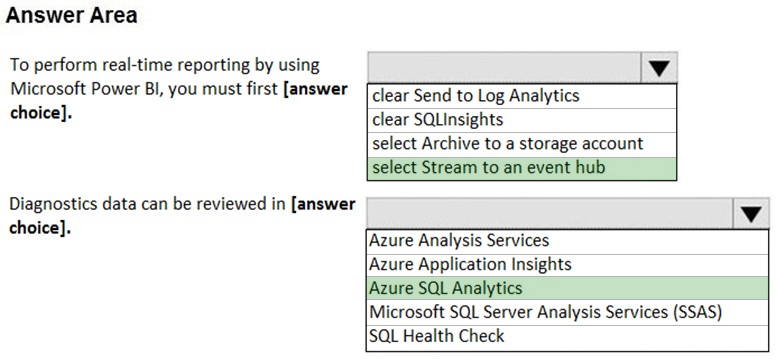
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.
Hot Area: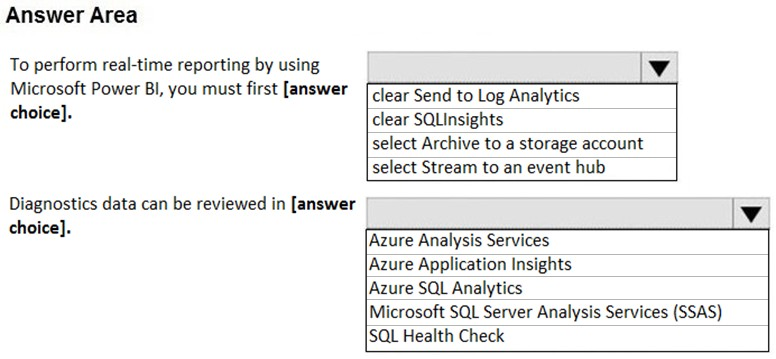
Correct Answer:
Note: This question is part of series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
Your company has an on-premises Active Directory Domain Services (AD DS) domain and an established Azure Active Directory (Azure AD) environment.
Your company would like users to be automatically signed in to cloud apps when they are on their corporate desktops that are connected to the corporate network.
You need to enable single sign-on (SSO) for company users.
Solution: Install and configure an Azure AD Connect server to use password hash synchronization and select the Enable single sign-on option.
Does the solution meet the goal?
Correct Answer:
A
You have an Azure subscription that contains a custom application named Application1. Application1 was developed by an external company named Fabrikam,
Ltd. Developers at Fabrikam were assigned role-based access control (RBAC) permissions to the Application1 components. All users are licensed for the
Microsoft 365 E5 plan.
You need to recommend a solution to verify whether the Fabrikam developers still require permissions to Application1. The solution must meet the following requirements:
✑ To the manager of the developers, send a monthly email message that lists the access permissions to Application1.
✑ If the manager does not verify an access permission, automatically revoke that permission.
✑ Minimize development effort.
What should you recommend?
Correct Answer:
D
Note: This question is part of series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
Your company has an on-premises Active Directory Domain Services (AD DS) domain and an established Azure Active Directory (Azure AD) environment.
Your company would like users to be automatically signed in to cloud apps when they are on their corporate desktops that are connected to the corporate network.
You need to enable single sign-on (SSO) for company users.
Solution: Install and configure an Azure AD Connect server to use pass-through authentication and select the Enable single sign-on option.
Does the solution meet the goal?
Correct Answer:
A