Note: This question is part of series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have an Azure Active Directory (Azure AZD) tenant named contoso.com. The tenant contains a group named Group1. Group1 contains all the administrative user accounts.
You discover several login attempts to the Azure portal from countries where administrative users do NOT work.
You need to ensure that all login attempts to the Azure portal from those countries require Azure Multi-Factor Authentication (MFA).
Solution: Implement Azure AD Privileged Identity Management.
Does this solution meet the goal?
Correct Answer:
A
Your company has several Azure subscriptions that are part of a Microsoft Enterprise Agreement.
The company's compliance team creates automatic alerts by using Azure Monitor.
You need to recommend a solution to apply the alerts automatically when new subscriptions are added to the Enterprise Agreement.
What should you include in the recommendation?
Correct Answer:
E
You store web access logs data in Azure Blob storage.
You plan to generate monthly reports from the access logs.
You need to recommend an automated process to upload the data to Azure SQL Database every month.
What should you include in the recommendation?
Correct Answer:
B
Your company has the offices shown in the following table.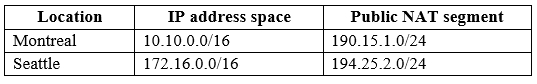
The network contains an Active Directory domain named contoso.com that is synced to Azure Active Directory (Azure AD).
All users connect to an application hosted in Microsoft 365.
You need to recommend a solution to ensure that all the users use Azure Multi-Factor Authentication (MFA) to connect to the application from one of the offices.
What should you include in the recommendation?
Correct Answer:
D
HOTSPOT -
You have an Azure subscription that contains 300 Azure virtual machines that run Windows Server 2016.
You need to centrally monitor all warning events in the System logs of the virtual machines.
What should you include in the solutions? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Hot Area: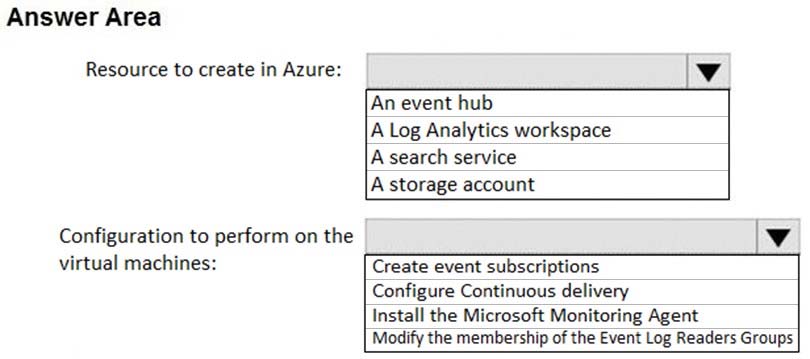
Correct Answer:
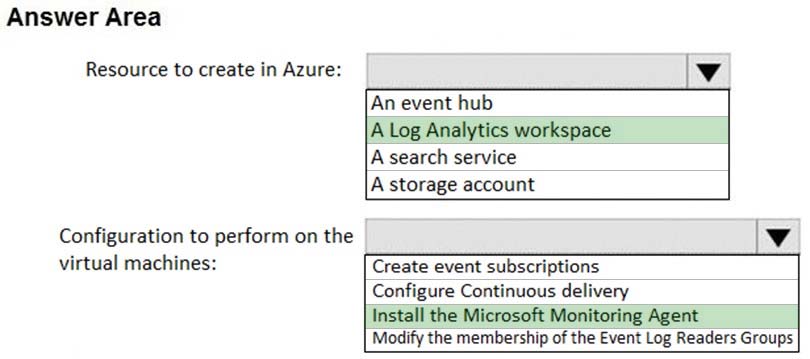
References:
https://docs.microsoft.com/en-us/azure/azure-monitor/platform/data-sources-windows-events https://docs.microsoft.com/en-us/azure/azure-monitor/platform/agent-windows