Your company has the divisions shown in the following table.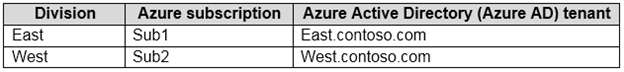
Sub1 contains an Azure web app that runs an ASP.NET application named App1. App1 uses the Microsoft identity platform (v2.0) to handle user authentication.
Users from east.contoso.com can authenticate to App1.
You need to recommend a solution to allow users from west.contoso.com to authenticate to App1.
What should you recommend for the west.contoso.com Azure AD tenant?
Correct Answer:
D
There are several components that make up the Microsoft identity platform:
✑ OAuth 2.0 and OpenID Connect standard-compliant authentication service
Application management portal: A registration and configuration experience in the Azure portal, along with the other Azure management capabilities.
You register an application using the App registrations experience in the Azure portal so that your app can be integrated with the Microsoft identity platform and call Microsoft Graph.
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/develop/v2-overview https://docs.microsoft.com/en-us/graph/auth-register-app-v2
You have an Azure Active Directory (Azure AD) tenant named contoso.com that has a security group named Group1. Group1 is configured for assigned membership. Group1 has 50 members, including 20 guest users.
You need to recommend a solution for evaluating the membership of Group1. The solution must meet the following requirements:
✑ The evaluation must be repeated automatically every three months.
✑ Every member must be able to report whether they need to be in Group1.
✑ Users who report that they do not need to be in Group1 must be removed from Group1 automatically.
✑ Users who do not report whether they need to be in Group1 must be removed from Group1 automatically.
What should you include in the recommendation?
Correct Answer:
A
In Azure Active Directory (Azure AD), you can create complex attribute-based rules to enable dynamic memberships for groups. Dynamic group membership reduces the administrative overhead of adding and removing users.
When any attributes of a user or device change, the system evaluates all dynamic group rules in a directory to see if the change would trigger any group adds or removes. If a user or device satisfies a rule on a group, they are added as a member of that group. If they no longer satisfy the rule, they are removed.
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/users-groups-roles/groups-dynamic-membership
Your company purchases an app named App1.
You need to recommend a solution to ensure that App1 can read and modify access reviews.
What should you recommend?
Correct Answer:
B
The app must be registered. You can register the application in the Azure Active Directory admin center.
The Azure AD access reviews feature has an API in the Microsoft Graph endpoint.
You can register an Azure AD application and set it up for permissions to call the access reviews API in Graph.
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/develop/quickstart-register-app
You have 200 resource groups across 20 Azure subscriptions.
Your companyג€™s security policy states that the security administrator must verify all assignments of the Owner role for the subscriptions and resource groups once a month. All assignments that are not approved by the security administrator must be removed automatically. The security administrator must be prompted every month to perform the verification.
What should you use to implement the security policy?
Correct Answer:
B
Azure Active Directory (Azure AD) access reviews enable organizations to efficiently manage group memberships, access to enterprise applications, and role assignments. User's access can be reviewed on a regular basis to make sure only the right people have continued access.
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/governance/access-reviews-overview