HOTSPOT -
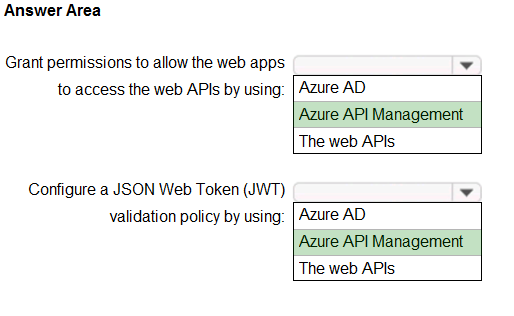
Your company has 20 web APIs that were developed in-house.
The company is developing 10 web apps that will use the web APIs. The web apps and the APIs are registered in the companyג€™s Azure Active Directory (Azure
AD) tenant. The web APIs are published by using Azure API Management.
You need to recommend a solution to block unauthorized requests originating from the web apps from reaching the web APIs. The solution must meet the following requirements:
✑ Use Azure AD-generated claims.
✑ Minimize configuration and management effort.
What should you include in the recommendation? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Hot Area: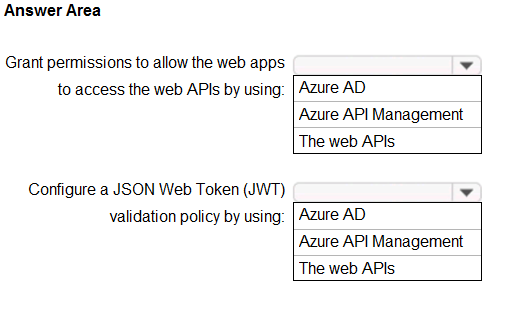
Correct Answer:
HOTSPOT -
You need to design a resource governance solution for an Azure subscription. The solution must meet the following requirements:
✑ Ensure that all ExpressRoute resources are created in a resource group named RG1.
✑ Delegate the creation of the ExpressRoute resources to an Azure Active Directory (Azure AD) group named Networking.
✑ Use the principle of least privilege.
What should you include in the solution? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Hot Area: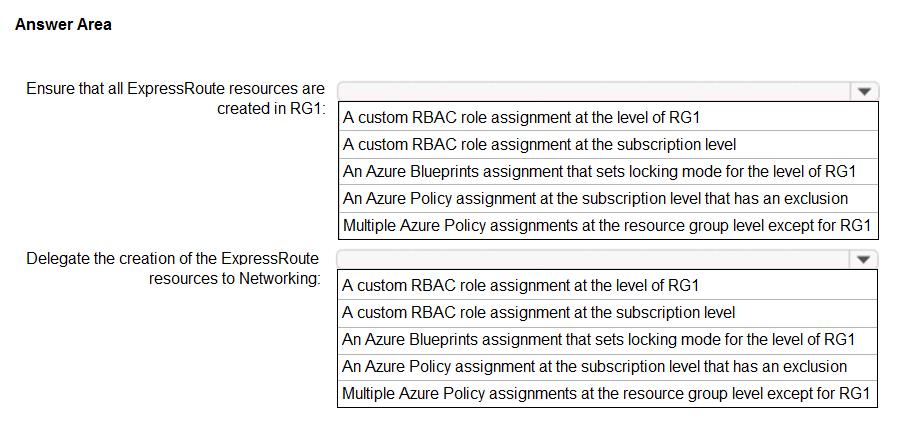
Correct Answer:
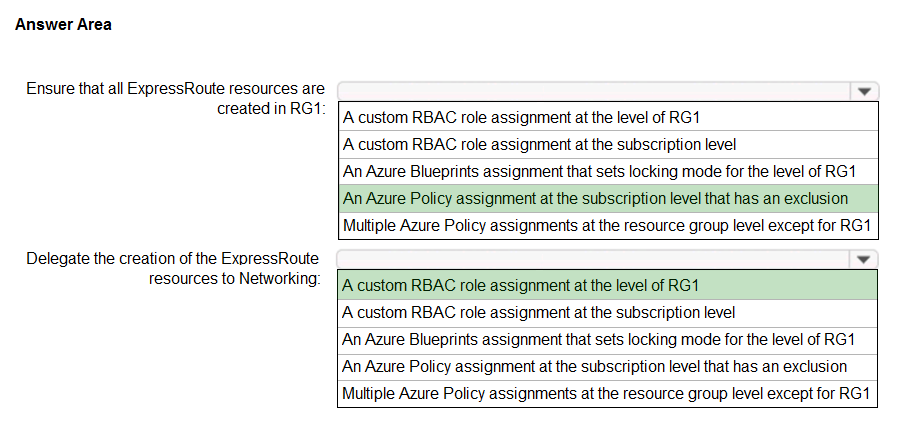
Box 1: An Azure policy assignment at the subscription level that has an exclusion
Box 2: A custom RBAC role assignment at the level of RG1
Azure role-based access control (Azure RBAC) is the authorization system you use to manage access to Azure resources. To grant access, you assign roles to users, groups, service principals, or managed identities at a particular scope.
Reference:
https://docs.microsoft.com/en-us/azure/governance/policy/tutorials/create-and-manage
You have an Azure Active Directory (Azure AD) tenant and Windows 10 devices.
You configure a conditional access policy as shown in the exhibit. (Click the Exhibit tab.)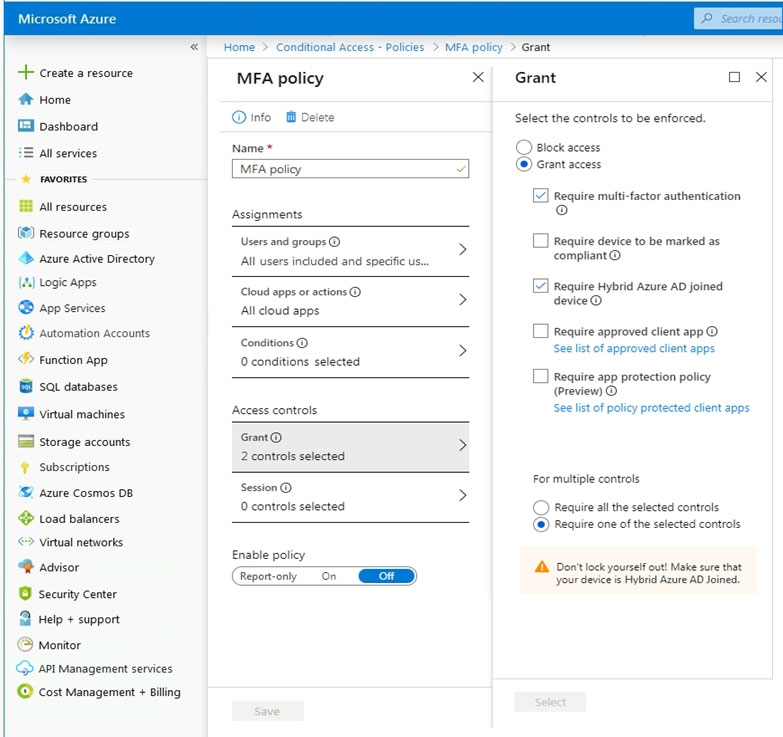
What is the result of the policy?
Correct Answer:
B
Either the device should be joined to Azure AD or MFA must be used.
HOTSPOT -
You have an Azure Active Directory (Azure AD) tenant.
You plan to use Azure Monitor to monitor user sign-ins and generate alerts based on specific user sign-in events.
You need to recommend a solution to trigger the alerts based on the events.
What should you include in the recommendation? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Hot Area: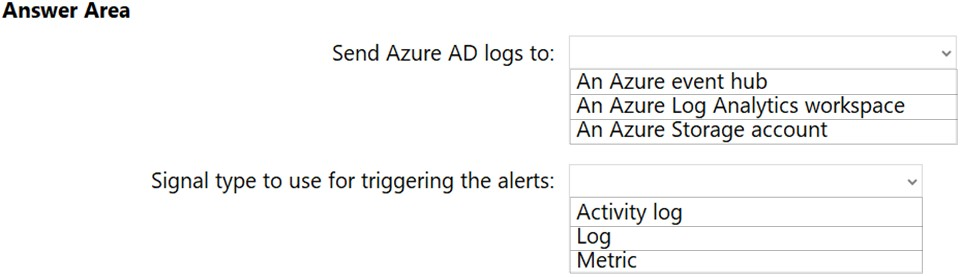
Correct Answer:
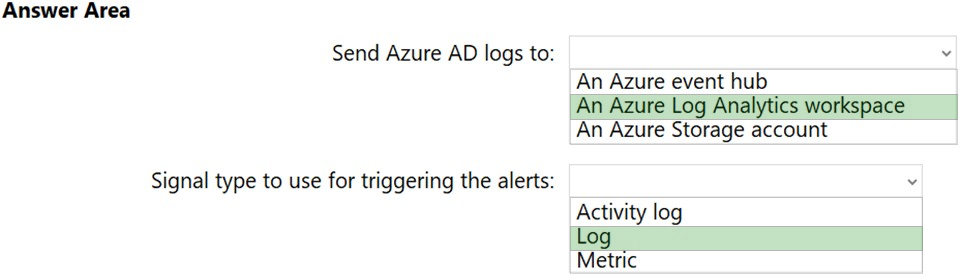
Box 1: An Azure Log Analytics workspace
To be able to create an alert we send the Azure AD logs to An Azure Log Analytics workspace.
Note: You can forward your AAD logs and events to either an Azure Storage Account, an Azure Event Hub, Log Analytics, or a combination of all of these.
Box 2: Log -
Ensure Resource Type is an analytics source like Log Analytics or Application Insights and signal type as Log.
Reference:
https://4sysops.com/archives/how-to-create-an-azure-ad-admin-login-alert/ https://docs.microsoft.com/en-us/azure/azure-monitor/platform/alerts-log