DRAG DROP -
Your on-premises network contains a server named Server1 that runs an ASP.NET application named App1.
You have a hybrid deployment of Azure Active Directory (Azure AD).
You need to recommend a solution to ensure that users sign in by using their Azure AD account and Azure Multi-Factor Authentication (MFA) when they connect to App1 from the internet.
Which three Azure services should you recommend be deployed and configured in sequence? To answer, move the appropriate services from the list of services to the answer area and arrange them in the correct order.
Select and Place: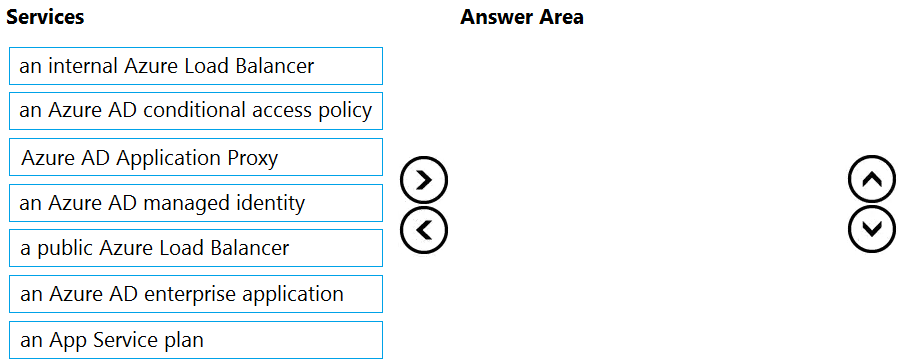
Correct Answer:
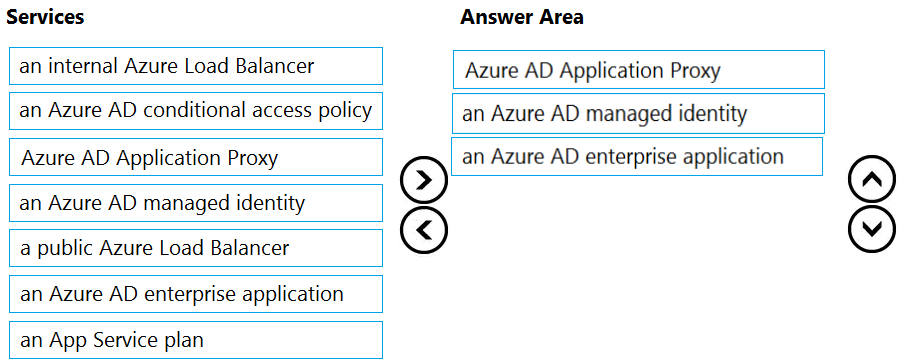
Step 1: Azure AD Application proxy
Azure AD Application Proxy is a prerequisite for a scenario with an on-premises legacy applications published for cloud access,
Note: Application Proxy is a feature of Azure AD that enables users to access on-premises web applications from a remote client. Application Proxy includes both the Application Proxy service which runs in the cloud, and the Application Proxy connector which runs on an on-premises server.
Step 2: an Azure AD managed identity
Microsoftג€™s identity solutions span on-premises and cloud-based capabilities. These solutions create a common user identity for authentication and authorization to all resources, regardless of location. We call this hybrid identity.
Step 3: an Azure AD conditional access policy
Conditional Access is the tool used by Azure Active Directory to bring signals together, to make decisions, and enforce organizational policies. Conditional Access is at the heart of the new identity driven control plane.
With hybrid identity to Azure AD and hybrid identity management these scenarios become possible.
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/authentication/howto-mfa-getstarted https://docs.microsoft.com/en-us/azure/active-directory/conditional-access/overview
A company named Contoso, Ltd. has an Azure Active Directory (Azure AD) tenant that is integrated with Microsoft 365 and an Azure subscription.
Contoso has an on-premises identity infrastructure. The infrastructure includes servers that run Active Directory Domain Services (AD DS), Active Directory
Federation Services (AD FS), Azure AD Connect, and Microsoft Identity Manager (MIM).
Contoso has a partnership with a company named Fabrikam, Inc. Fabrikam has an Active Directory forest and a Microsoft 365 tenant. Fabrikam has the same on- premises identity infrastructure components as Contoso.
A team of 10 developers from Fabrikam will work on an Azure solution that will be hosted in the Azure subscription of Contoso. The developers must be added to the Contributor role for a resource group in the Contoso subscription.
You need to recommend a solution to ensure that Contoso can assign the role to the 10 Fabrikam developers. The solution must ensure that the Fabrikam developers use their existing credentials to access resources.
What should you recommend?
Correct Answer:
C
Trust configurations - Configure trust from managed forests(s) or domain(s) to the administrative forest
✑ A one-way trust is required from production environment to the admin forest.
✑ Selective authentication should be used to restrict accounts in the admin forest to only logging on to the appropriate production hosts.
Reference:
https://docs.microsoft.com/en-us/windows-server/identity/securing-privileged-access/securing-privileged-access-reference-material
You are designing an Azure governance solution.
All Azure resources must be easily identifiable based on the following operational information: environment, owner, department, and cost center.
You need to ensure that you can use the operational information when you generate reports for the Azure resources.
What should you include in the solution?
Correct Answer:
D
You use Azure Policy to enforce tagging rules and conventions. By creating a policy, you avoid the scenario of resources being deployed to your subscription that don't have the expected tags for your organization. Instead of manually applying tags or searching for resources that aren't compliant, you create a policy that automatically applies the needed tags during deployment.
Note: Organizing cloud-based resources is a crucial task for IT, unless you only have simple deployments. Use naming and tagging standards to organize your resources for these reasons:
Resource management: Your IT teams will need to quickly locate resources associated with specific workloads, environments, ownership groups, or other important information. Organizing resources is critical to assigning organizational roles and access permissions for resource management.
Reference:
https://docs.microsoft.com/en-us/azure/cloud-adoption-framework/decision-guides/resource-tagging https://docs.microsoft.com/en-us/azure/azure-resource-manager/management/tag-policies
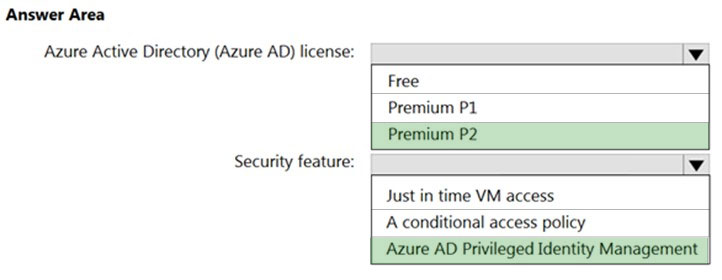
HOTSPOT -
You are designing an access policy for your company.
Occasionally, the developers at the company must stop, start, and restart Azure virtual machines. The development team changes often.
You need to recommend a solution to provide the developers with the required access to the virtual machines. The solution must meet the following requirements:
✑ Provide permissions only when needed.
✑ Use the principle of least privilege.
✑ Minimize costs.
What should you include in the recommendation? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Hot Area: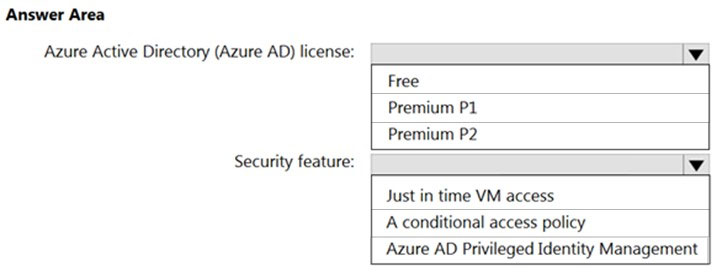
Correct Answer: